

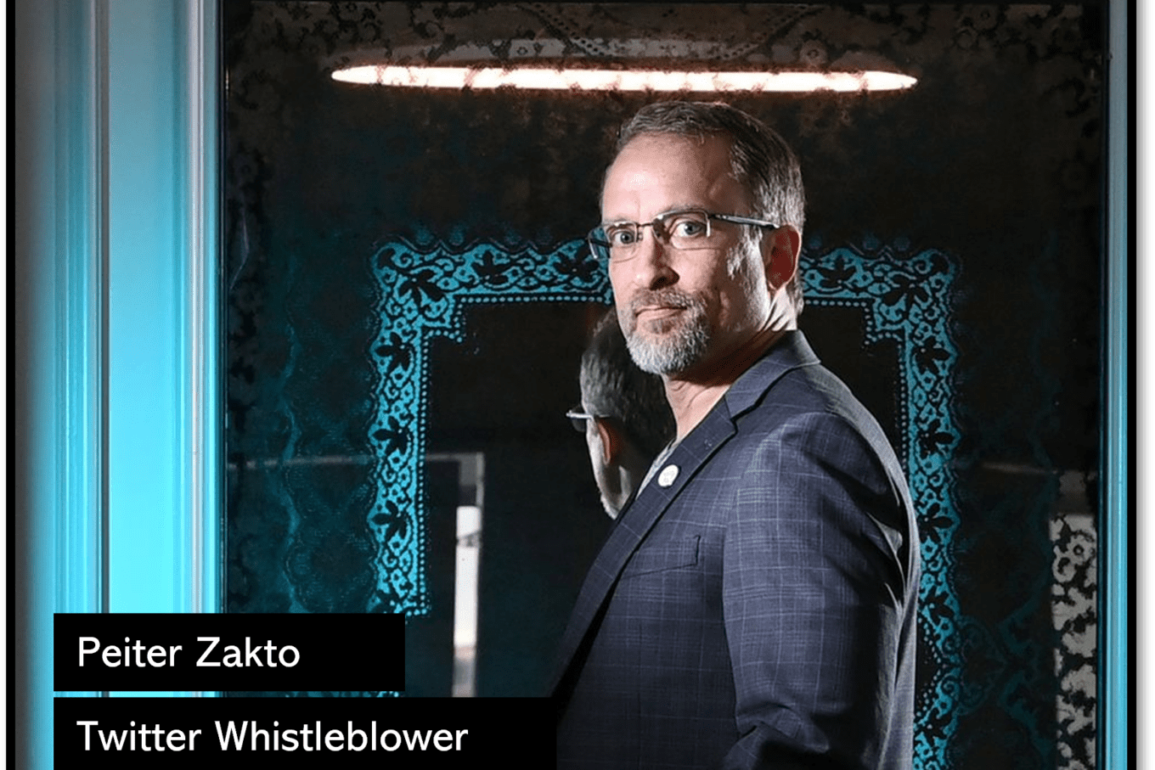
Twitter’s former security chief has raised serious questions about the company’s security practices, saying it poses a national security risk. Peiter “Mudge” Zatko, Twitter’s former head of security, says the company has misled regulators about its security measures in his whistleblower complaint. According to Zatko, Twitter’s dealings with other countries could be putting the United States’ national security at risk.
Read: Sony launches new DualSense Edge pro controller for PS5
“A few months before CTO Parag Agrawal was promoted to CEO, Agrawal suggested to Mudge that Twitter should consider ceding to the Russian Federation’s censorship and surveillance demands as a way to grow users in Russia,” the complaint states.
During that time, Russia tried to force large tech companies, including Twitter, to open local offices in the country before its invasion of Ukraine.
In Zatko’s complaint filed with the Securities and Exchange Commission, the Department of Justice and the Federal Trade Commission, he also accuses the company of violating the terms it had agreed to when it settled a privacy dispute with the FTC more than a decade ago. It claims that Twitter knew about its deficiencies, but didn’t manage to address than (or didn’t want to, in some cases).
“Twitter is grossly negligent in several areas of information security. If these problems are not corrected, regulators, media and users of the platform will be shocked when they inevitably learn about Twitter’s severe lack of security basics,” Zatko said.

This comes amid the Twitter-Musk drama, with Musk pulling out of the sale due to Twitter’s lack of transparency about the number of bots on the platform. He cites a source who allegedly said that Twitter was wary of determining the real number of bots on the website, because it “would harm the image and valuation of the company.”
Several institutions and congressional committees are now investigating the case.
